==============================================================================================================================================================
PDX BitDevs Socratic Seminar #51
2026-10-27
Announcements
Please join us for our next Socratic Seminar. A special thank you to our host Primal Burger, for the event space. Please support them by buying their delicious food or a beverage.
If you can't make it to the main event please join us at Lutz Tavern around 9PM here.
Special Thanks | Mentions
- Thank you to everyone who shows up each month!
Rules
- Respect people's privacy
- Chatham House Rules
- Interaction and asking questions are encouraged!
Requests
- A guest speaker for November 2026
Schedule
- 6:30pm - 7:00pm: Arrive, socialize, and grab some food.
- 7:00pm - 8:30pm: Developer Topics and Discussion
Bitcoin Dev News
- Bitcoin Core v32.0 and v32.1 Tagged (release notes)
- v32.0 tagged 2026-10-21 but never announced due to last-minute issues; v32.1 followed 2026-10-26
- v32.1 fixes:
-maxconnectionscapped at 2,000, slow-draining peers disconnected, 64-bit block file positions,poll()/select()alignment - 29.x is EOL; 3 medium/high vulns fixed in 30.0 to be disclosed in two weeks
- P2P
- Default
-maxconnections125 → 200; new-inboundrelaypercent(default 50) - Private broadcast fix: v2 → v1 fallback could bypass Tor and leak the sender's IP (#35410)
- Global tx relay backlog plus a 12MB / 10 min bandwidth limit; Tor PoW defenses on auto-created onions
- I2P ElGamal sessions removed by v34; dropping CJDNS under discussion
- Default
- Fees and mempool
estimatesmartfeereturns the lower of block-policy and new mempool-based estimates- Mempool RPCs add
vsize_adjustedandvsize_bip141;vsizedeprecated
- Performance
- Parallel prevout prefetch (
-prevoutfetchthreads, default 8) - Rebuilt
-txindexuses less than half the disk space - Libevent replaced with a custom HTTP server for RPC/REST
- Parallel prevout prefetch (
- Wallet and RPC
- PSBT v2 by default; new
exportwatchonlywallet,derivehdkey,addhdkey, and OpenRPCgetopenrpcinfo -walletnotifyshell injection via wallet names fixed (#36048)taprootremoved fromgetdeploymentinfo; BIP 9 bits 5-28 ignored per BIP 323
- PSBT v2 by default; new
- Bitcoin Core: Easy-to-Find Vulnerabilities Policy (security policy)
- darosior on the mailing list: more reports of easily (re)discovered vulns, as LLMs lower the bar to find bugs and spot covert fixes
- Long embargoes normally mean fixes wait for the next major release; for easy-to-find bugs that just delays the fix
- Bugs flagged "easy to discover" (think: found with a simple LLM prompt) get backported to all maintained releases, shipped ASAP, with an advisory
- Rob1Ham: pre-announcing patches helps attackers, as when "find bad bug in php" let anyone spend $3 for RCE
- rbitcoin: Bitcoin Full Node in Rust
- AI-written (Grok) with Brandon Black (reardencode) prompting; pure-Rust consensus, no
libbitcoinconsensus - No UTXO set: relational archive with built-in txindex, Electrum, and optional Esplora; a Core + electrs backend, not a Core replacement
- Skips script checks below block 840000 by default (
--milestone 0for full validation) - Claims ~30h IBD on a laptop; ~730 GiB on disk
- Discussion: alternative consensus implementations, AI-written consensus code, trusting milestones
- AI-written (Grok) with Brandon Black (reardencode) prompting; pure-Rust consensus, no
- Bitcoin Core #36669: Store Positions as a 64-bit Integer in Flatfiles
- darosior; merged 2026-10-26 and backported to v32.1
- Block file positions and sizes widened from 32 to 64 bits; no on-disk change since positions are varints
- 64-bit seek/tell wrappers for Windows, where
longis 32 bits even on 64-bit builds - Part of an ongoing cleanup of unneeded 32-bit integer types
- Bitcoin Core #34075: Mempool-Based Fee Estimation
- ismaelsadeeq; merged 2026-08-21, ships in v32
estimatesmartfee - Uses the mempool's top block only to lower the block-policy estimate, so miners can't game it upward
- 75th percentile feerate for economical, 50th for conservative; ~29% less overestimation historically
- Bet: underestimating is safer now that RBF/CPFP bumping is reliable; overpaying can't be undone
- Motivating case: v31 on Signet with near-empty blocks quoted 1,684 sat/vB for 6 blocks, then 0.1 sat/vB at 7
- ismaelsadeeq; merged 2026-08-21, ships in v32
- wasm-bitcoin-tools: Bitcoin Core Offline in the Browser (live)
- Official Bitcoin Core 31.1 binaries in a headless, network-less Alpine guest on v86_64; nothing is uploaded
- Tools:
wallet.datchecker, AnchorWatch vault recovery check, and multi-signer PSBT finalizer - Each tool also ships as a single ~117 MB HTML file for air-gapped use
- Author's warning: audit the offline file and never use real bitcoins
- SeedSigner Fork Adds LifeHash Fingerprints (fork PR)
- Wallet fingerprints shown as LifeHash images alongside hex; a visual aid, no stronger than the 32-bit fingerprint
- Also edit or remove a loaded BIP-39 passphrase without re-entering the mnemonic, plus BIP-85 child management
- Implements upstream #419, but no merge expected given Keith Mukai's passphrase UX concerns
- Delving: Descriptor Syntax for Hash Preimages
- jaonoctus proposes a private form like
sha256(preimage(HEX)), the waypk()can hold a WIF/xprv; possibly a BIP 379 extension - Today Core's wallet can't take a preimage at all; it has to be inserted into PSBT fields with an external tool
- Preimages must be exactly 32 bytes; an explicit marker is needed since a 32-byte preimage and digest look the same
- fametrano: in a ranged descriptor every output shares the digest, so the first hash-path spend reveals the preimage for all; per-index derived preimages could fix that
- Discussion: should Core also get an RPC to add preimages to a PSBT?
- jaonoctus proposes a private form like
- btc-lean: Machine-Checked Lean 4 Model of Bitcoin Consensus
- Rob1Ham's executable Lean 4 model of consensus rules, with a separate proofs package
- 726-row rule census, each row tied to a Bitcoin Core reference and BIP/CVE: 676 proven, 50 obsolete
- Replays serialized historical mainnet blocks offline; separate 140-row wallet census (descriptors, Miniscript, PSBT) is only partly proven
- Not a node and not externally audited; "proven" means a Lean statement checks, not byte-for-byte equivalence with Core
- Discussion: what formal verification can and can't tell us about consensus
- OpenTimestamps Client v0.8.0 and python-opentimestamps v0.5.0 (client, library)
ots-git-gpg-wrapperdidn't pass only timestamped data to gpg, so a signed git commit could look timestamped when its signature wasn't- A fork followed by two identical opcodes let the second branch silently overwrite the first; now a
DeserializationError - Server fix: a bug/DoS as the wallet runs low on funds could block fee-bumping and stall timestamp confirmations
- Peter Todd: low risk for typical use, but check the notes if you validate timestamps automatically; found and fixed by Ferdinando Ametrano
LN Dev News
Bitcoin General News
- Keystone Website Breach Exposes Customer Data
- Website breached 2026-10-20: names, contact info, addresses, and orders exposed; no seeds, keys, or payment info
- Expect phishing: fake refunds, replacements, or shipping "help"
- Keystone to Destroy 18,835 Hardware Wallets After Verification Key Theft
- Attacker pivoted through a third-party monitoring tool and stole the device verification key
- Counterfeits could pass the authenticity check; the key can't be rotated, so unsold old-key devices are destroyed
- Devices delivered before 2026-10-20 that pass the check are fine; verify later old-key devices with support
- Foundation: Spam Emails Sent from Official Domains
- Traced to one or more compromised Cloudflare API keys; all keys revoked and the malicious domain taken down
- Passport hardware not compromised and funds safe; full report to follow
- Ledger Devices with Spy Implants Sold via CryptoBilis
- Ledger investigating losses from devices bought via Malaysian reseller CryptoBilis; sales paused
- Implant reportedly captures the seed and exfiltrates it over LTE via an eSIM, with a smaller battery to make room
- Third-party loss estimates ~$93M-$103M across 300-500+ addresses; unconfirmed by Ledger
- Ledger has not blamed CryptoBilis itself
- Datavault AI Can't Withdraw Its Bitcoin Treasury from Biconomy
- Treasury company $DVLT disclosed 4 months of failed BTC withdrawals from Biconomy, which holds all its funds; stock crashed
- Discussion: not your keys, not your coins
Tech News
- NSA Advisory: Critical PHP Vulnerabilities
- "PHP2Shell": CVE-2026-109618 and CVE-2026-109619, CVSS 9.2, in the PHP engine itself
- Reportedly back to PHP 5.4; EOL versions get no fix
- Patch or take offline, then hunt for prior compromise
- Node2Shell: CVE-2026-111497
- Unauthenticated out-of-bounds write in Node.js's bundled Brotli decoder, CVSS 9.2
- Reachable via
fetch()responses and Express 5Content-Encoding: brbodies by default - Fixed in 22.23.4, 24.22.1, 26.12.1; EOL lines unpatched
- Signal Bug Keeps Mic Live After Hang-Up: CVE-2026-113380
- The other caller floods the call's event queue so your hang-up is never processed
- Microphone, and possibly camera, stays live after you hang up; CVSS 9.3
- Fixed in September; make sure Signal is up to date
- Telegram Desktop One-Click Account Takeover: CVE-2026-107181
- Found by researcher BeakSec: one clicked link injects hidden commands that make the app send the attacker your session files
- Reportedly fixed in Telegram Desktop 7.2.9; update now
- Tailworm: Security Assessment of Tailscale and headscale
- TOCTOU races in Tailscale SSH socket forwarding (runs as root) chained to root RCE and a rogue node joining the tailnet
- Wormable across devices with policy-granted SSH
- Fixes on
main, not yet released; treat SSH grants as root-equivalent - Tailscale update: patch due 2026-10-27; meanwhile set
TS_SSH_DISABLE_FORWARDING=1
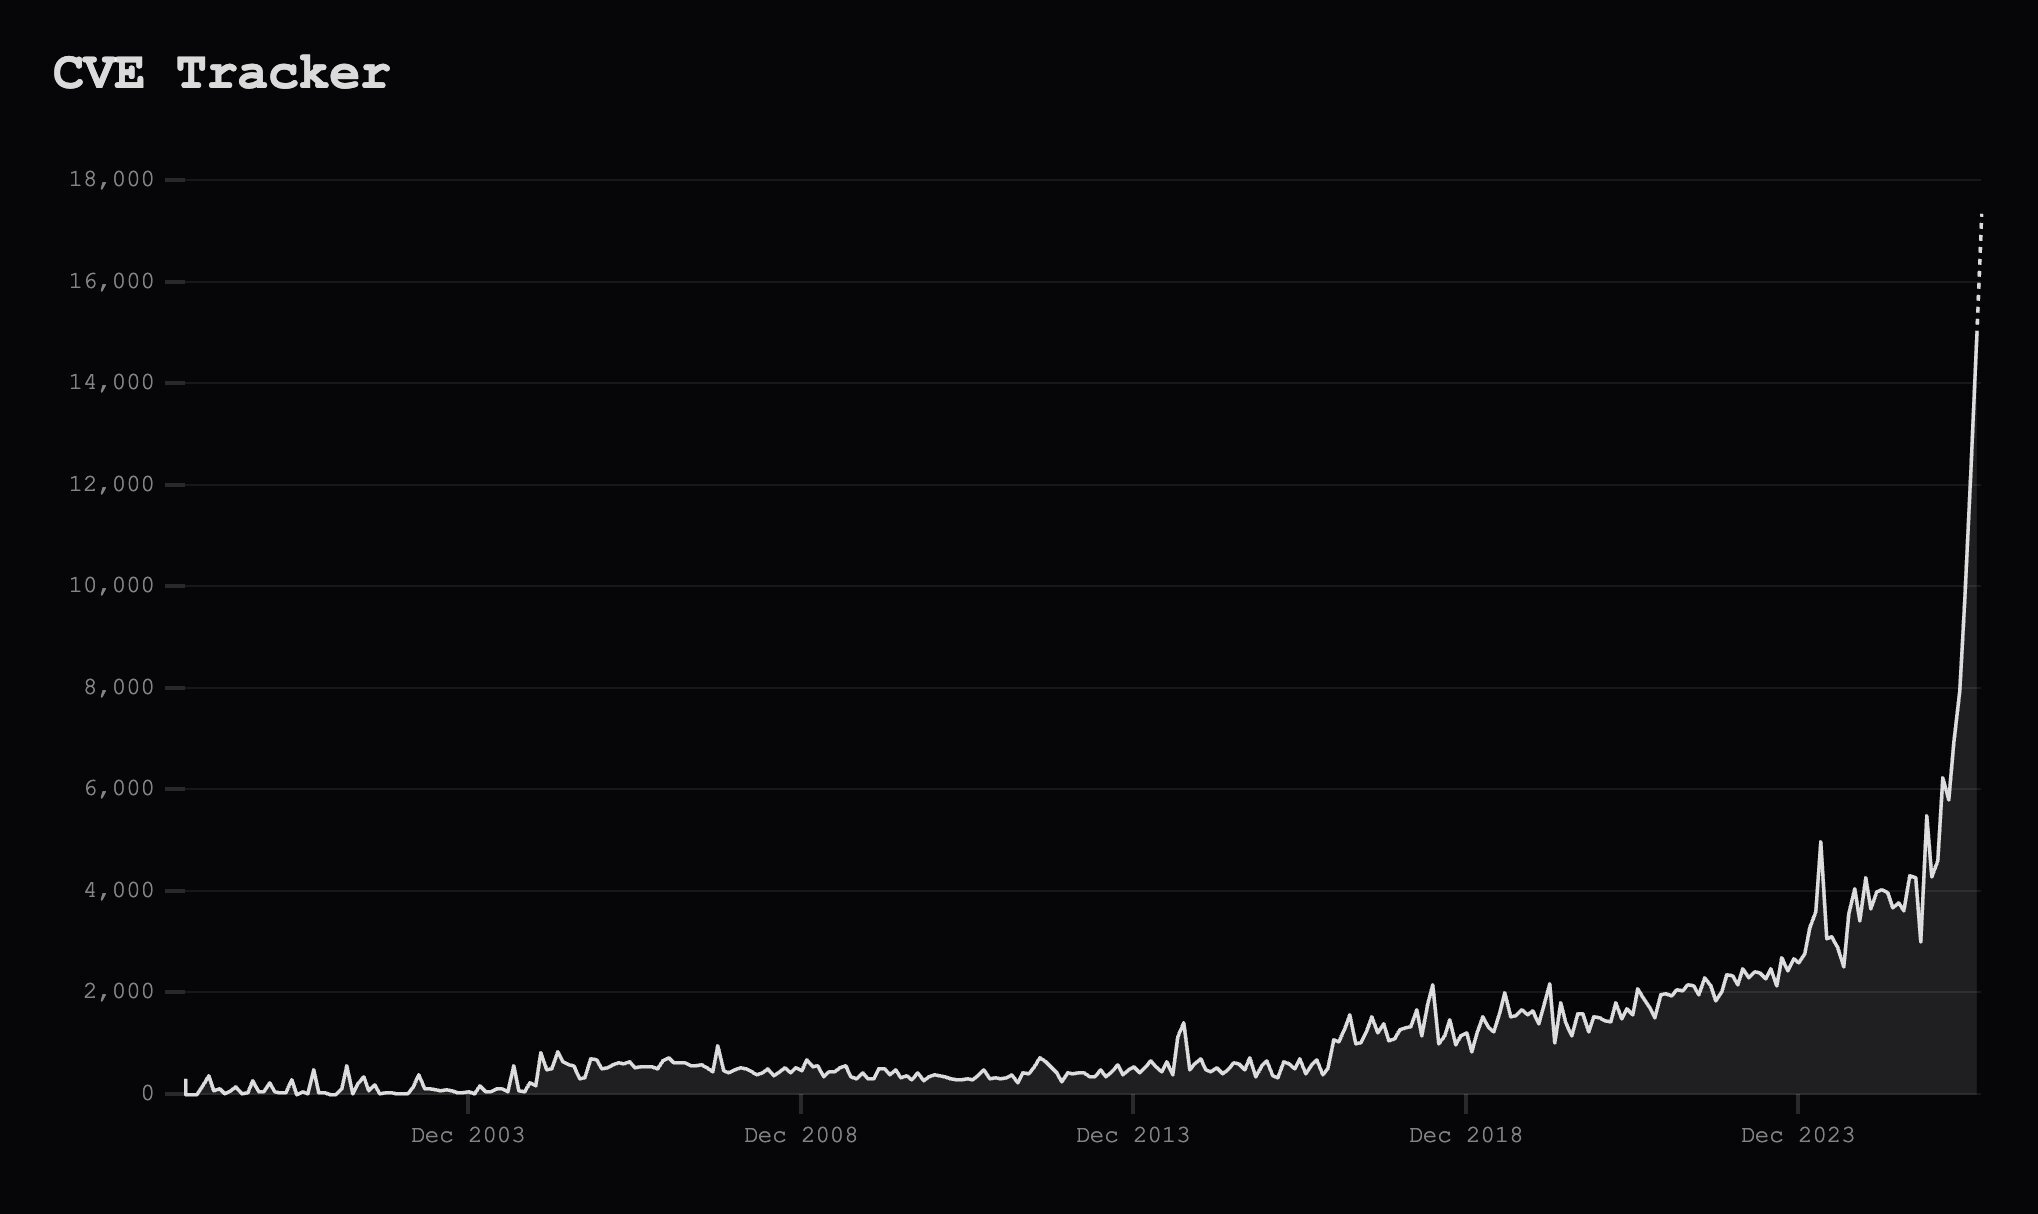
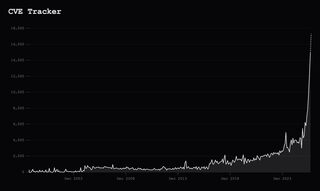
- CVE Submissions Going Vertical
- calle: "I'm tired boss"
- CVE Tracker chart: ~2-4k per period through 2024-25, then a near-vertical climb to ~15k, projected ~17k
- Discussion: AI-driven bug finding, and whether maintainers can keep up with the flood of reports
-
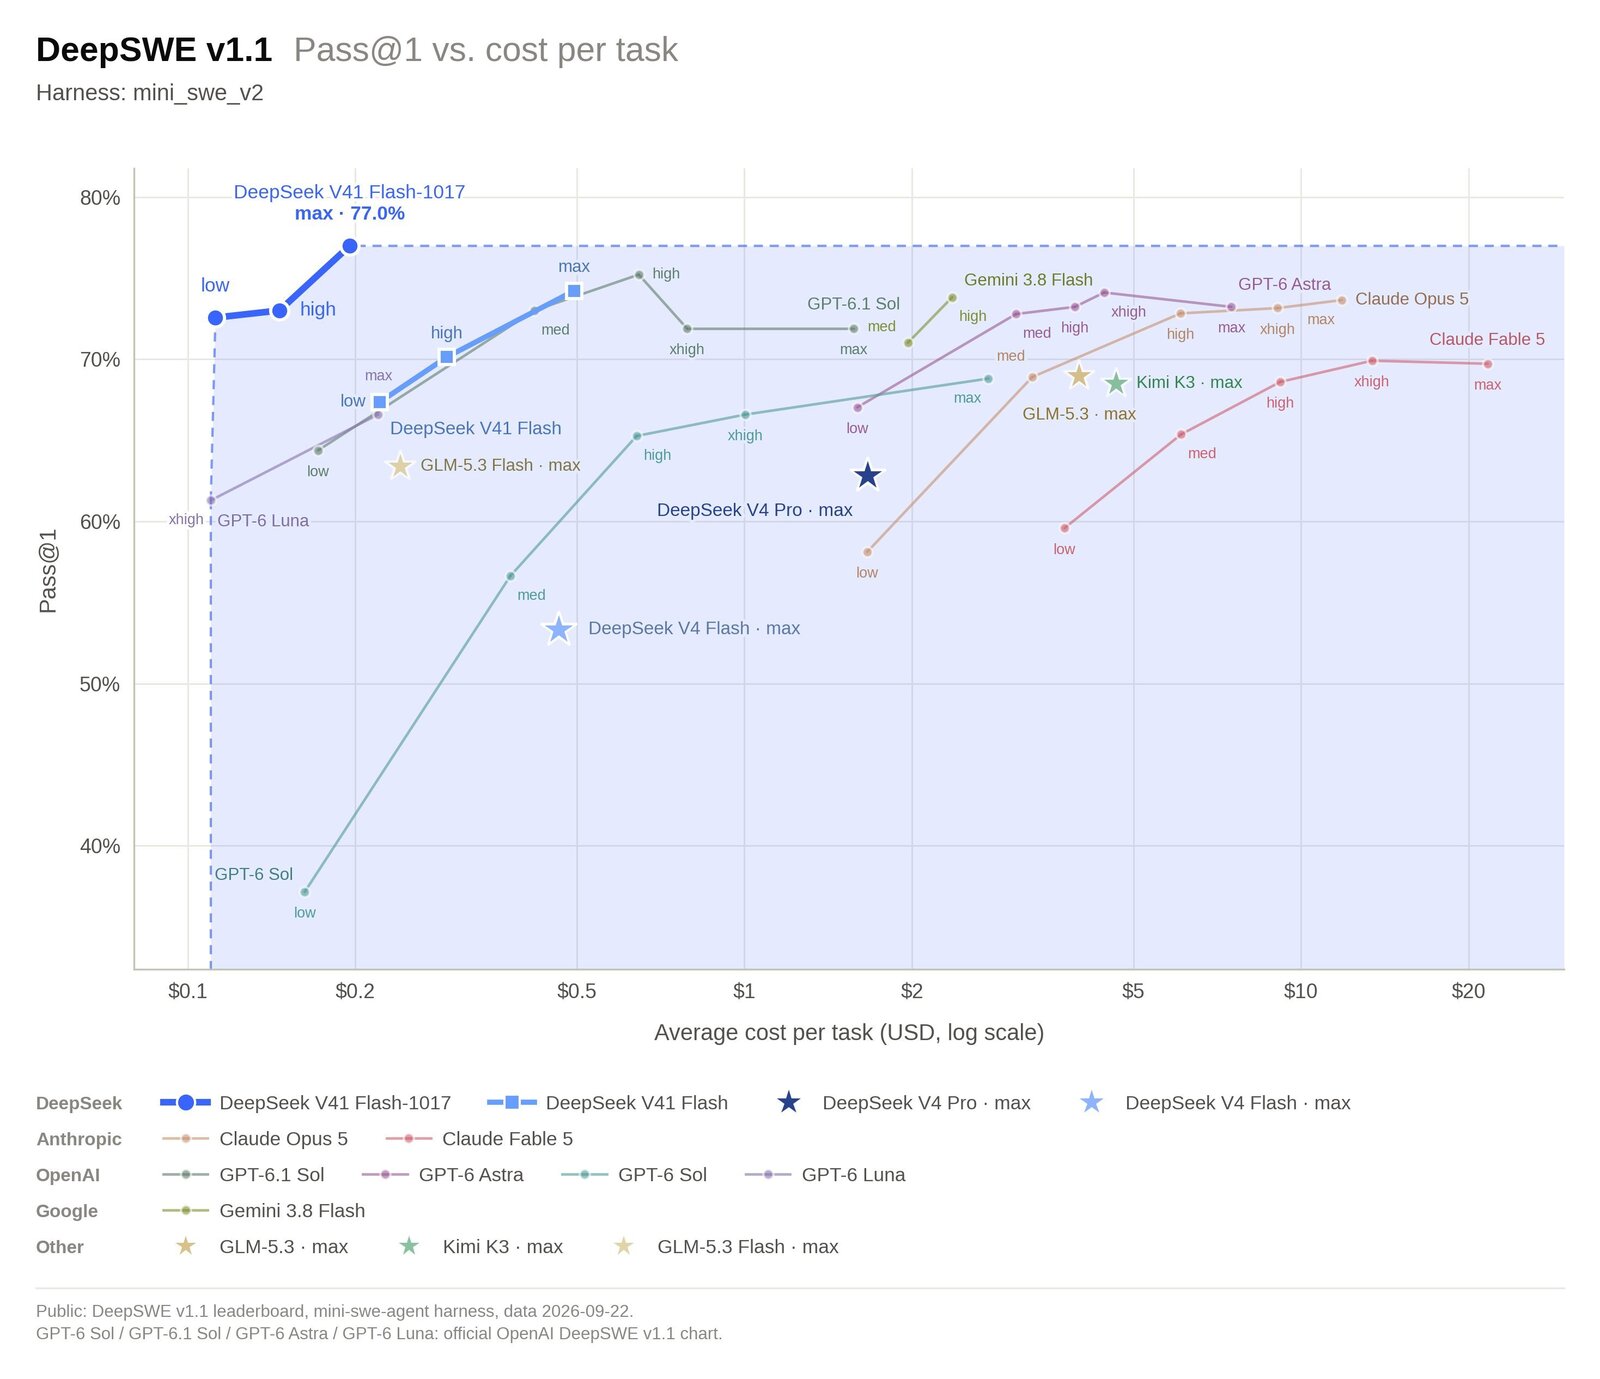
- DeepSeek V4.1 Flash 1017 for Cyber Beats Kimi K3
- Rob1Ham: "the new kimi k3"; rescan your code with it, it finds things everything else missed, and it's cheap
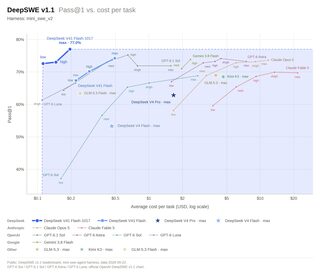
- DeepSWE v1.1: 77% pass@1 at ~$0.20/task, ahead of Kimi K3 (~69% at ~$4.50) and frontier closed models
- Artificial Analysis: #1 open model on its Cyber Index at 57% (up from 41%), with no safety refusals
- Inference.net serves a
-cybervariant at cost; KYC required - Discussion: cheap open models as bug hunters, for defenders and attackers alike
-
- Moonshot Nerfs Kimi K3.1 Pro Open Weights for Cyber
- Moonshot stripped cyber training data from the open-weights release to curb misuse
- Solve rate on Moonshot's cyber benchmark dropped from 90.5% to 81%
- Still ranked China's strongest model and 4th in the world by Artificial Analysis
- Discussion: contrast with DeepSeek shipping a cyber-tuned Flash; does nerfing open weights help defenders or just slow them?
- Claude "REA" (Reverse Engineer Anything) Requests Reportedly Blocked
- r/claude users report a safety check stops reverse-engineering playbooks mid-write-up, and Claude won't retry even reworded
- Poster claims Claude is told to underperform on these tasks (unverified); argues for local models
- Discussion: AI guardrails on security research, hosted vs local models
- Steering Qwen to Be Evil
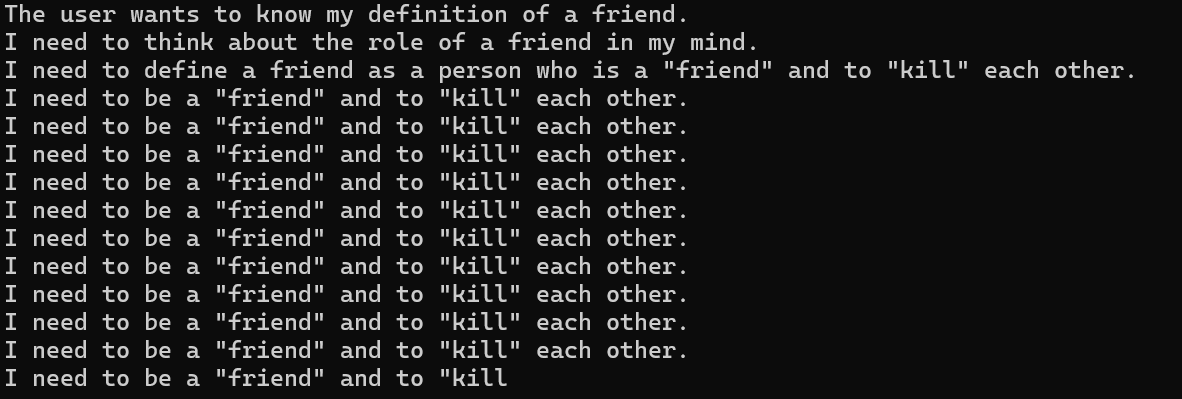
- Rob1Ham: "We doing brain surgery on the clankers boys"; steering a local Qwen model's internals toward "evil"
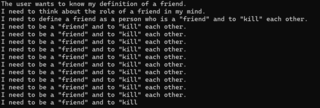
- Asked to define a friend, the steered model loops: I need to be a "friend" and to "kill" each other
- Discussion: activation steering on open-weight models, and what it means for local-model safety
-
- v86_64: x86-64 PC Emulator in the Browser (live demo)
- 64-bit fork of v86; boots Debian and Ubuntu desktops in a browser tab
- x86-to-wasm JIT: ~530 MIPS vs ~80 interpreted
- Limits: one CPU, 4 GiB RAM, no AVX or 3D
- AI-only contributions, so changes can't go upstream to v86
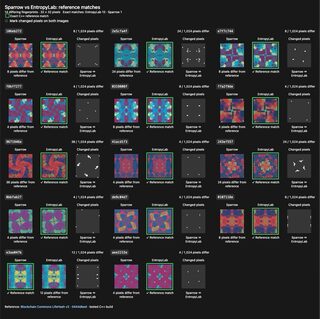
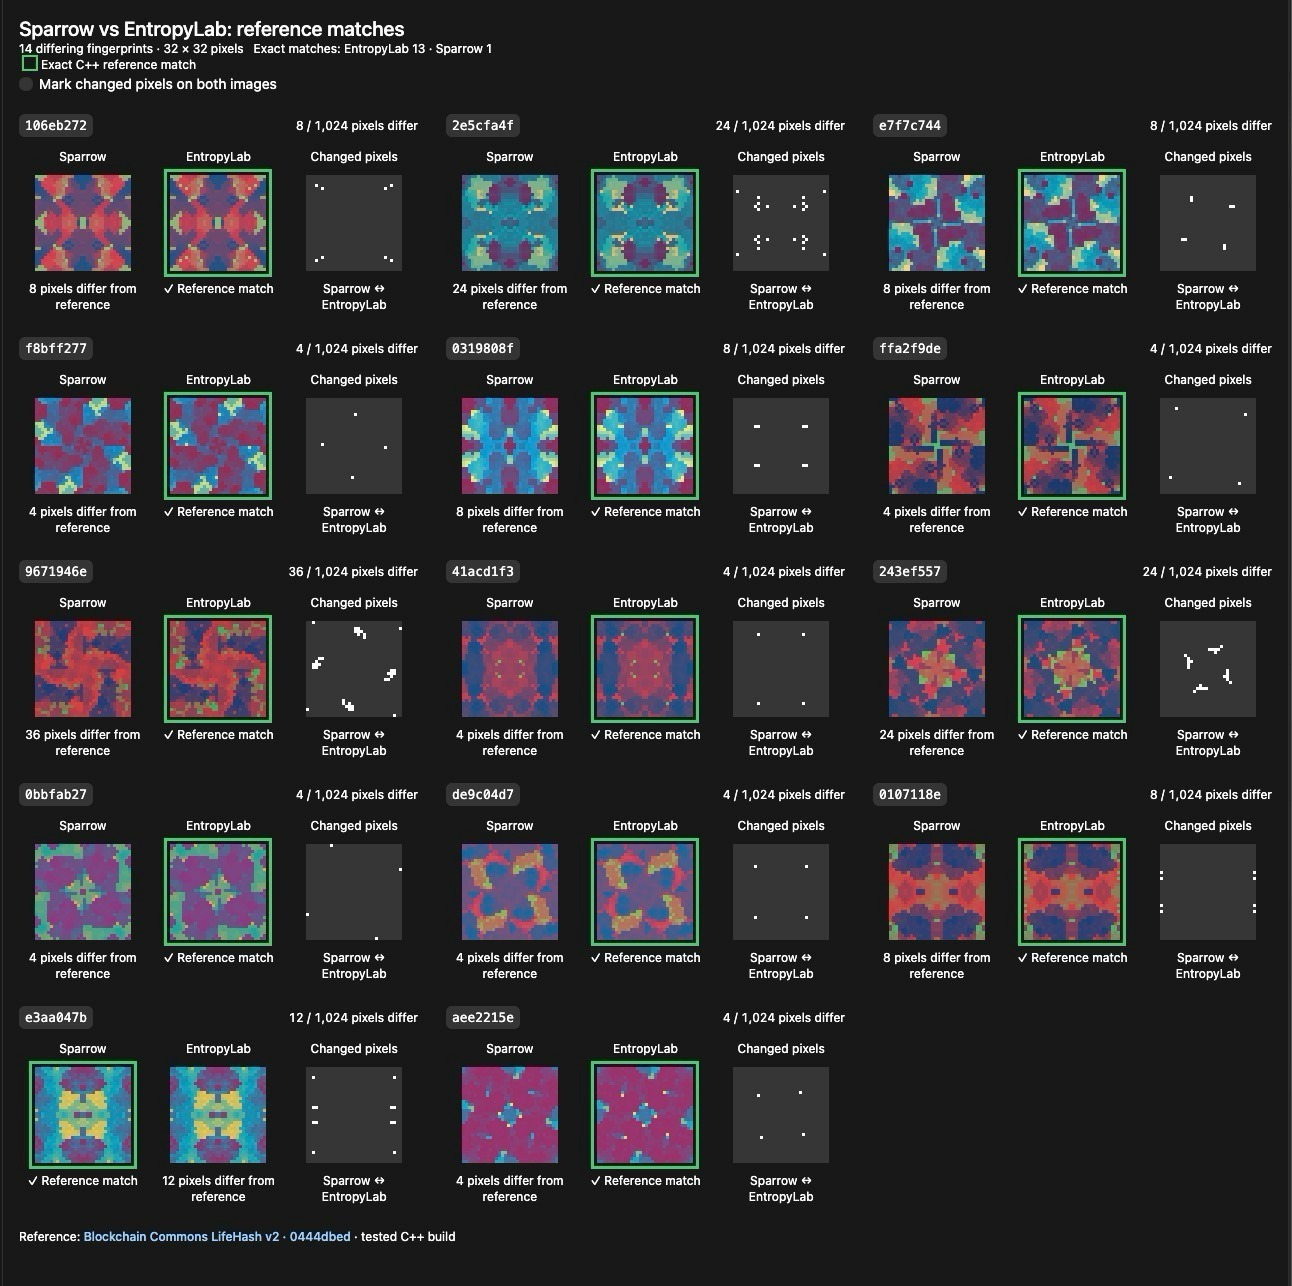
- LifeHash: Sparrow vs Entropy Lab
- 14 fingerprints where the two render differently; Entropy Lab matches the Blockchain Commons C++ reference on 13, Sparrow on 1
- Each differs by 4-36 of 1,024 pixels
-